Attachment encrypted
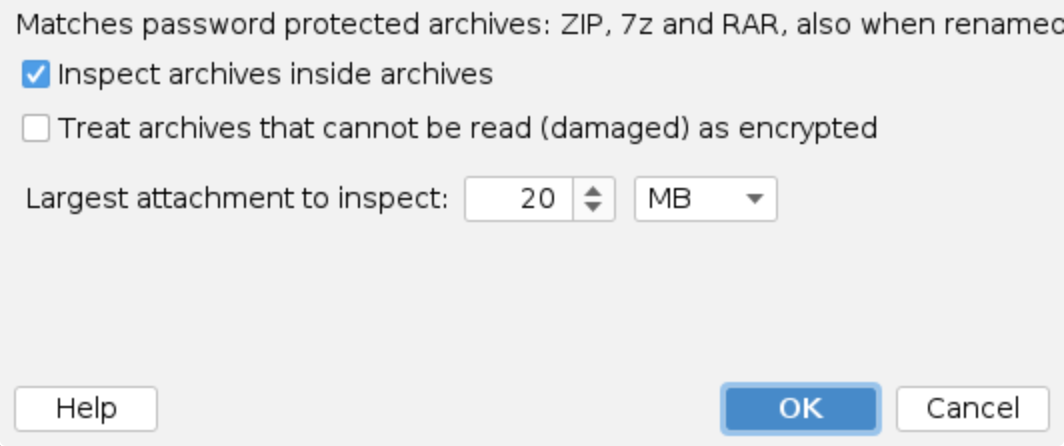
This condition matches messages that carry a password protected archive. Sending malware in an encrypted ZIP, with the password in the message body, is a common way to get it past antivirus scanning, since the scanner cannot look inside. Combined with the Block message action of a policy rule, the condition rejects such mail, and an exception lets trusted partners through.
A message matches when at least one of its attachments is a password protected archive. The condition is available in policy rules and disclaimer rules, as a condition and as an exception.
Supported archives
ZIP, 7z and RAR (4 and 5) archives are checked. An archive is recognised by the first bytes of its
content, never by its file name or content type, so a ZIP renamed to invoice.pdf is found too.
Only the archive headers are read: nothing is decrypted and no password is guessed. An archive counts as password protected when:
- any of its files is encrypted, or
- it hides even its file names - a 7z archive created with header encryption, or a RAR archive
created with encrypted file names (
rar -hp).
Encrypted PDF and Office documents are not detected by this condition.
Options
Inspect archives inside archives: When on (the default), archives inside archives are opened
too, up to three levels deep, so a password protected ZIP packed inside an ordinary ZIP, or inside
a .tar.gz, is found as well.
Treat archives that cannot be read (damaged) as encrypted: When on, an archive that is damaged, or cannot be read for another reason such as holding more than 10,000 entries, matches as if it were password protected. When off (the default), such an archive is ignored.
Largest attachment to inspect: Attachments larger than this are not inspected and do not match. The default is 20 MB. The same limit applies to a nested archive.
To stop large archives from slipping through uninspected, add an Attachment size condition to a separate rule.
Processing trace
The processing trace in the Events history says what the condition found, for example:
Attachment 'invoice.zip' (ZIP) is password protected: 'invoice.pdf.exe' is encrypted.
Attachment 'docs.7z' (7z) is password protected: 7z archive with encrypted file names.
Attachment 'report.zip' (ZIP) is not encrypted.
Attachment 'backup.zip' is larger than 20 MB, not inspected.
Examples
- Reject password protected archives: a policy rule with this condition and the Block message action.
- Let a partner send encrypted archives: add a Message sender exception with the partner's domain to the same rule.
- Warn recipients instead of blocking: a policy rule with this condition and the
Modify subject action, prefix
[ENCRYPTED ARCHIVE].
Additional resources
- Archive content - match archives by the files they hold
- Rules tester - attach a password protected archive to check the rule before enabling it